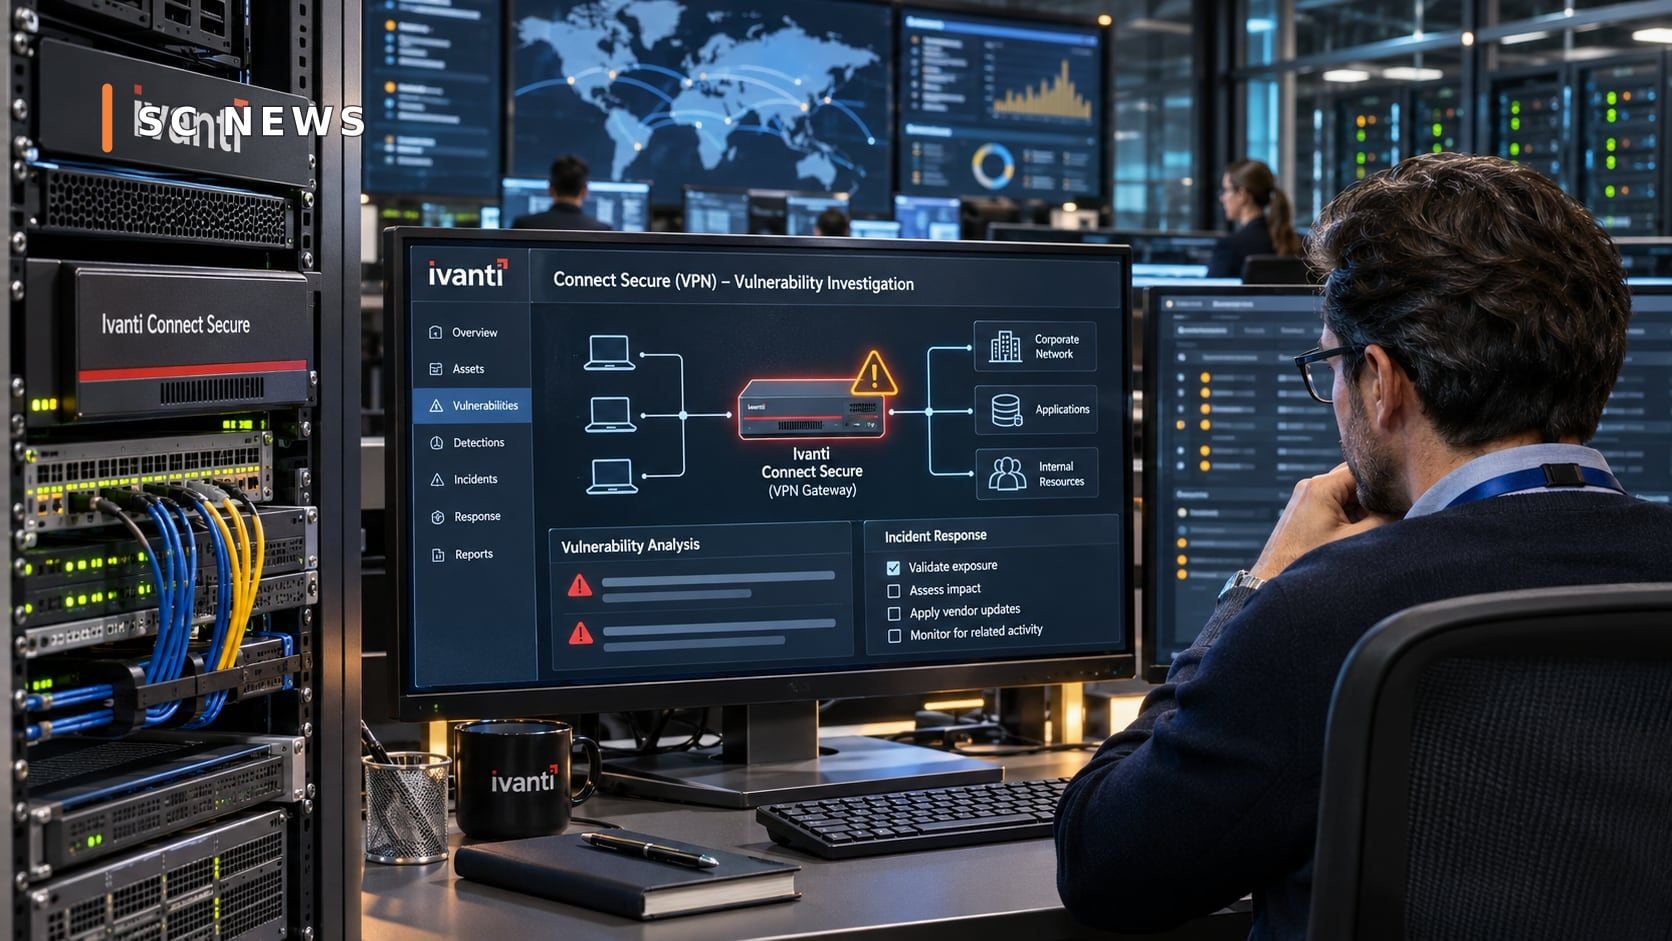
Organizations that rely on Ivanti's secure connectivity solutions face increased security risks following the disclosure of a series of vulnerabilities that were used in actual attacks against Connect Secure systems, products used to provide secure connectivity to corporate resources and internal networks.
The agency announced Cybersecurity and Infrastructure Security US CISA, on Friday, October 30, 2026, added two vulnerabilities affecting Ivanti Connect Secure to its list of vulnerabilities known to be exploited, known as Known Exploited Vulnerabilities, or KEV.
The move comes after security investigations revealed the possibility of merging several points Weakness to achieve high-authority access to targeted systems, which makes the issue go beyond the existence of a single vulnerability that can be dealt with in isolation from the rest of the components.
The Hacker News+1
Three vulnerabilities within one attack chain
The two vulnerabilities newly added to the list relate to identifiers:
- CVE-2026-111357: An identity verification flaw when executing a sensitive function could allow permission escalation in specific circumstances.
- CVE-2026-118527: A vulnerability related to generating identifiers or predictable values, which may allow files to be uploaded to known locations on the system after the necessary conditions are met. For exploitation.
Reports indicated that the two vulnerabilities were linked to a third flaw, CVE-2026-104935, which was previously disclosed and added to the CISA list in October.
According to the analysis published by the security company Volexity, the three vulnerabilities could be exploited within an attack chain to obtain root privileges, which are among the highest. Levels of control in target systems.
This does not mean that every single vulnerability gives an unauthorized attacker complete control; The main danger comes from the possibility of combining them under certain circumstances.
Attackers are looking for sensitive credentials
Investigations indicated the activity of a threat actor Tracked under the name UTA0576, the series exploited the vulnerabilities in operations aimed at obtaining information that could be used to expand the hack.
Observed activities included searching for login credentials and limited information related to Active Directory services, as well as trying to find keywords System administrators password and BitLocker recovery keys.
The importance of this information lies in the fact that it can be used to access other systems or expand the scope of the attack within the network.
The pattern of activity also shows that the absence of visible malware or a known attack file alone is not enough to rule out a breach; Some processes may focus on collecting data and conducting surveys within systems.
Security updates are now available
Ivanti has confirmed that fixes are available to address the vulnerabilities associated with the attack chain, including:
- 25.1.1.3
- 22.8R2.6
The appropriate version depends on the program branch The user is within the organization, so company guidelines should be reviewed before implementing the update.
It is also necessary to verify the integrity of the system before simply considering installing the patch the end of the problem; The update addresses the weakness, but it does not guarantee the removal of traces of a breach that may have occurred previously.
Processing deadlines and regulatory obligations
CISA has set dates to address some of the gaps in US federal civilian entities covered by its directives.
The dates included November 2 for remediation of CVE-2026-111357 and November 13 for remediation of CVE-2026-118527.
These dates do not apply as a commitment This is a general law for all companies around the world, but it indicates the level of priority given by US authorities to address these risks.
What does this mean for companies?
The incident highlighted the danger of remote communication devices when they are exposed to the Internet, especially as they may... It represents a crossing point to sensitive internal resources.
Appropriate defensive measures include inventorying affected systems, updating them according to company guidelines, reviewing access logs, examining elevated accounts, and looking for indicators of unusual activity.
It is preferable for security teams to handle this With these actions as an integrated response process, you don't just install a software update.
What's next?
Security agencies continue to monitor exploit activity and update their recommendations. The priority for organizations using Ivanti Connect Secure remains to check the status of installed versions, Apply appropriate corrections, and review potential prior exploitation.